Comprehensive testing
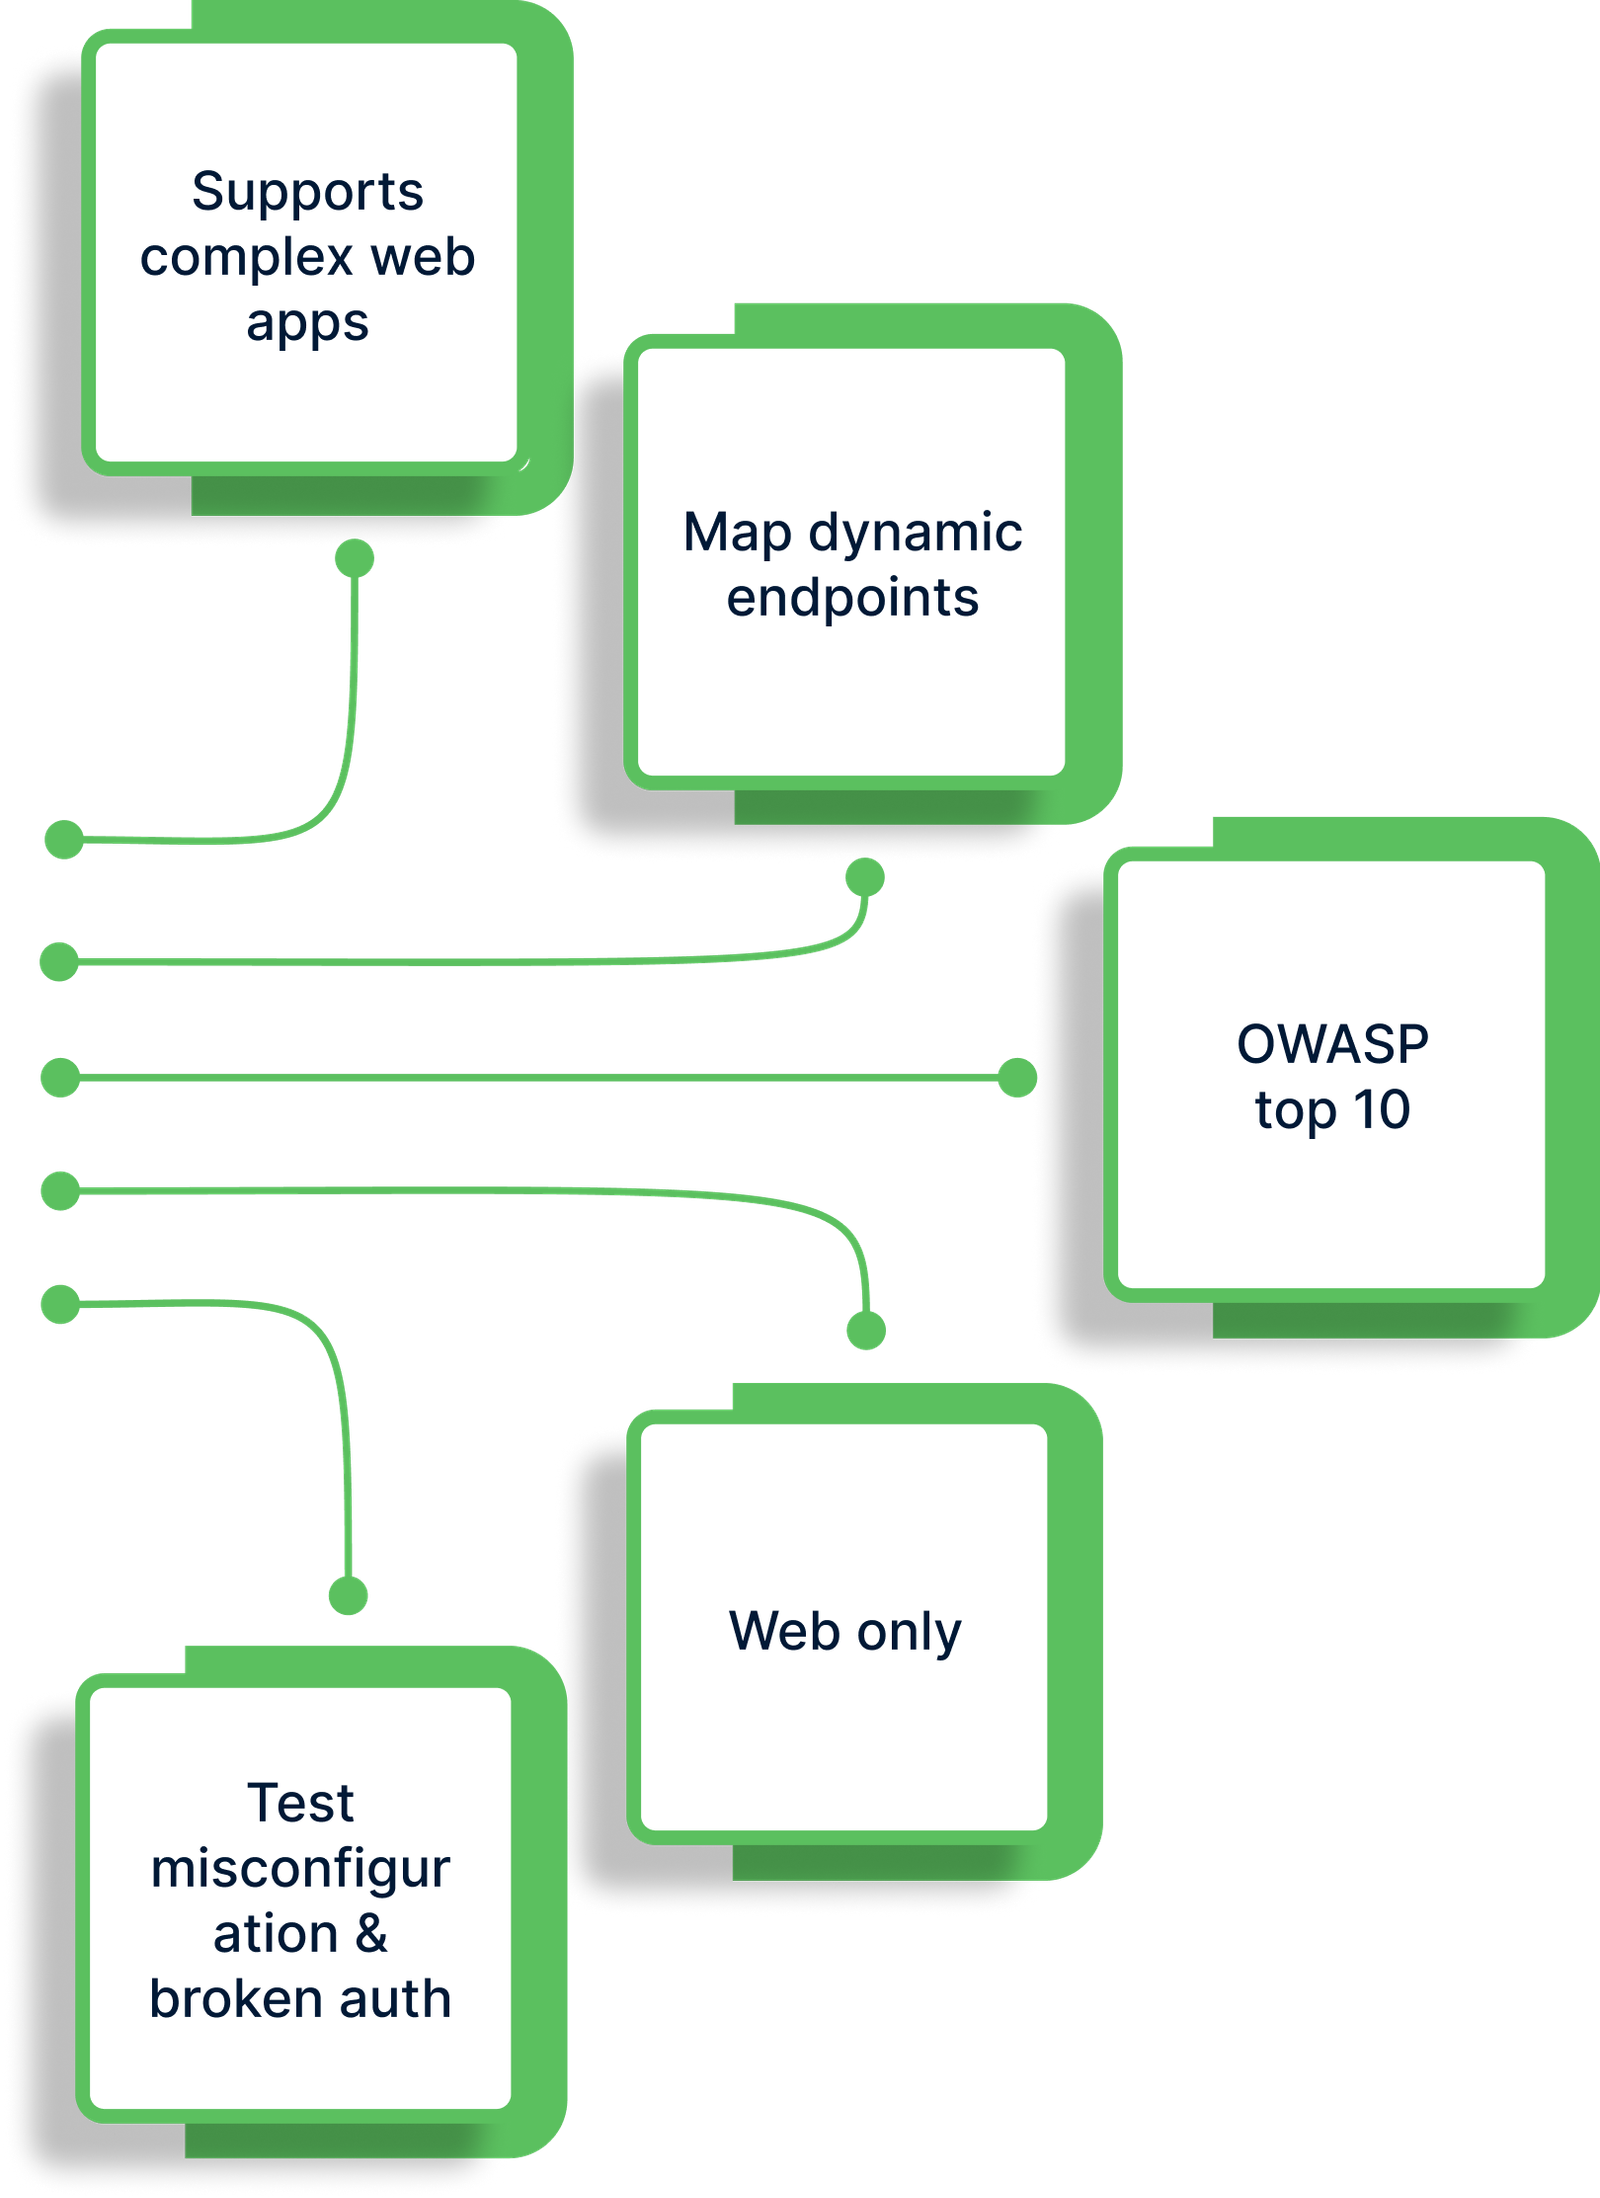
Quick scans plus pathways for deeper validation so critical issues do not slip through.
Welcome to Tulsi
Detect vulnerabilities before they become threats — then move from first scan to continuous assurance.
Automation, reporting, and expert-ready workflows — with a product experience built for speed and clarity.
Quick scans plus pathways for deeper validation so critical issues do not slip through.
Executive PDFs mapped to risk — built for ISO 27001, PCI-DSS, SOC 2 conversations.
Watch phases progress in real time and prioritize what to fix next.
Start free with one web app. Grow into Basic, Professional, Enterprise, or Elite.
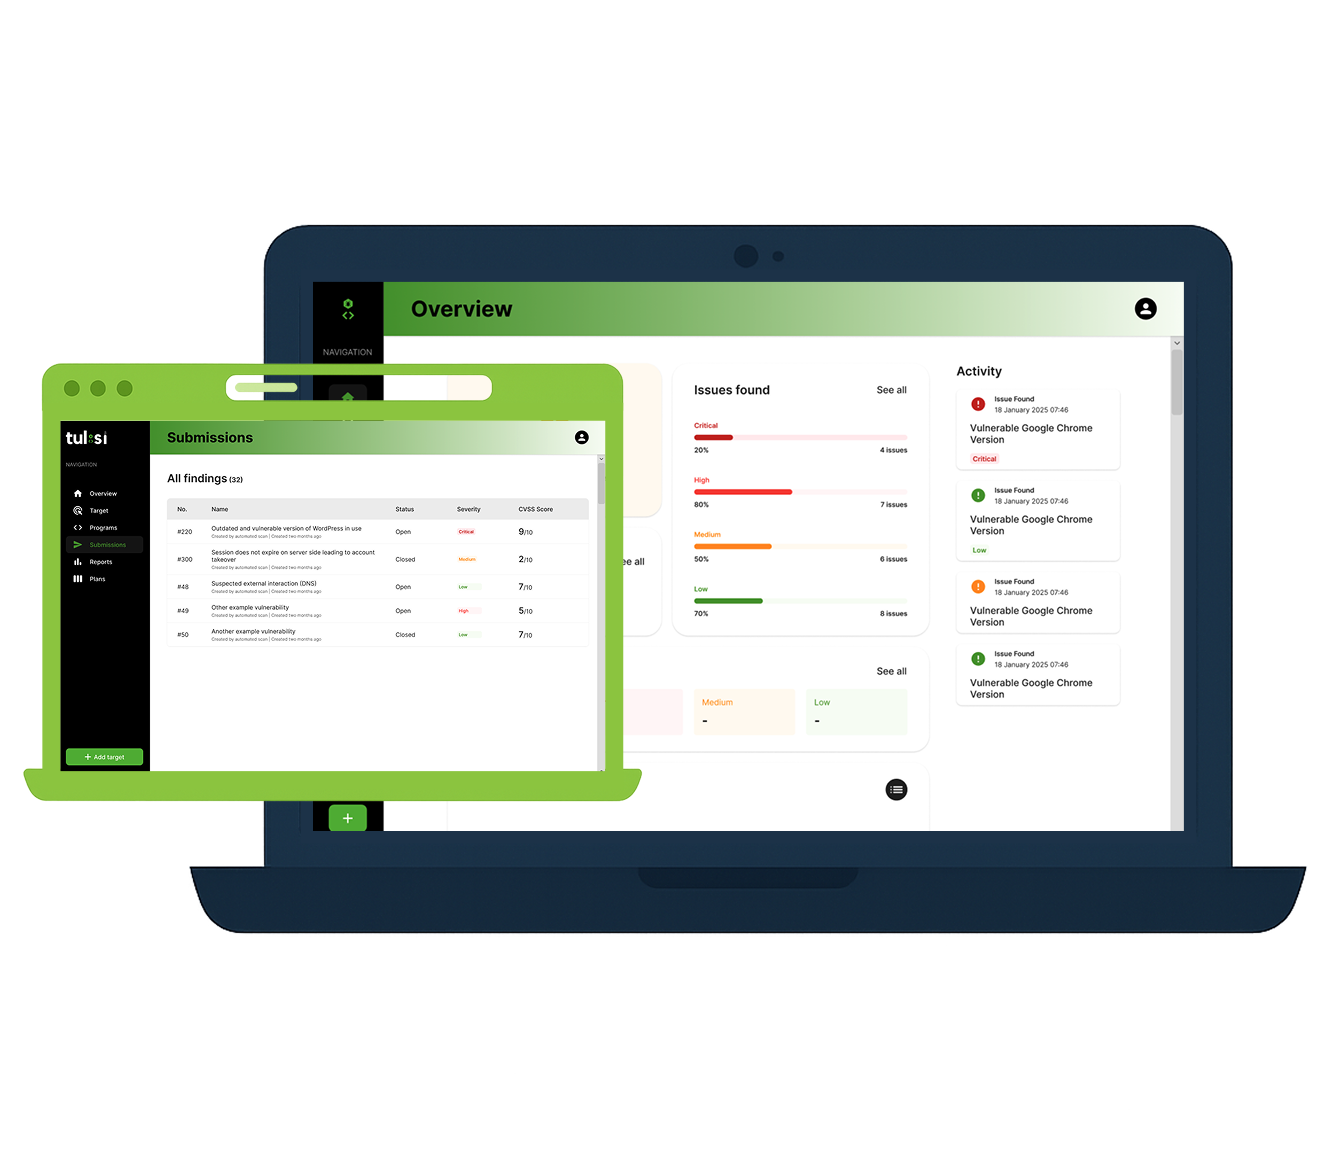
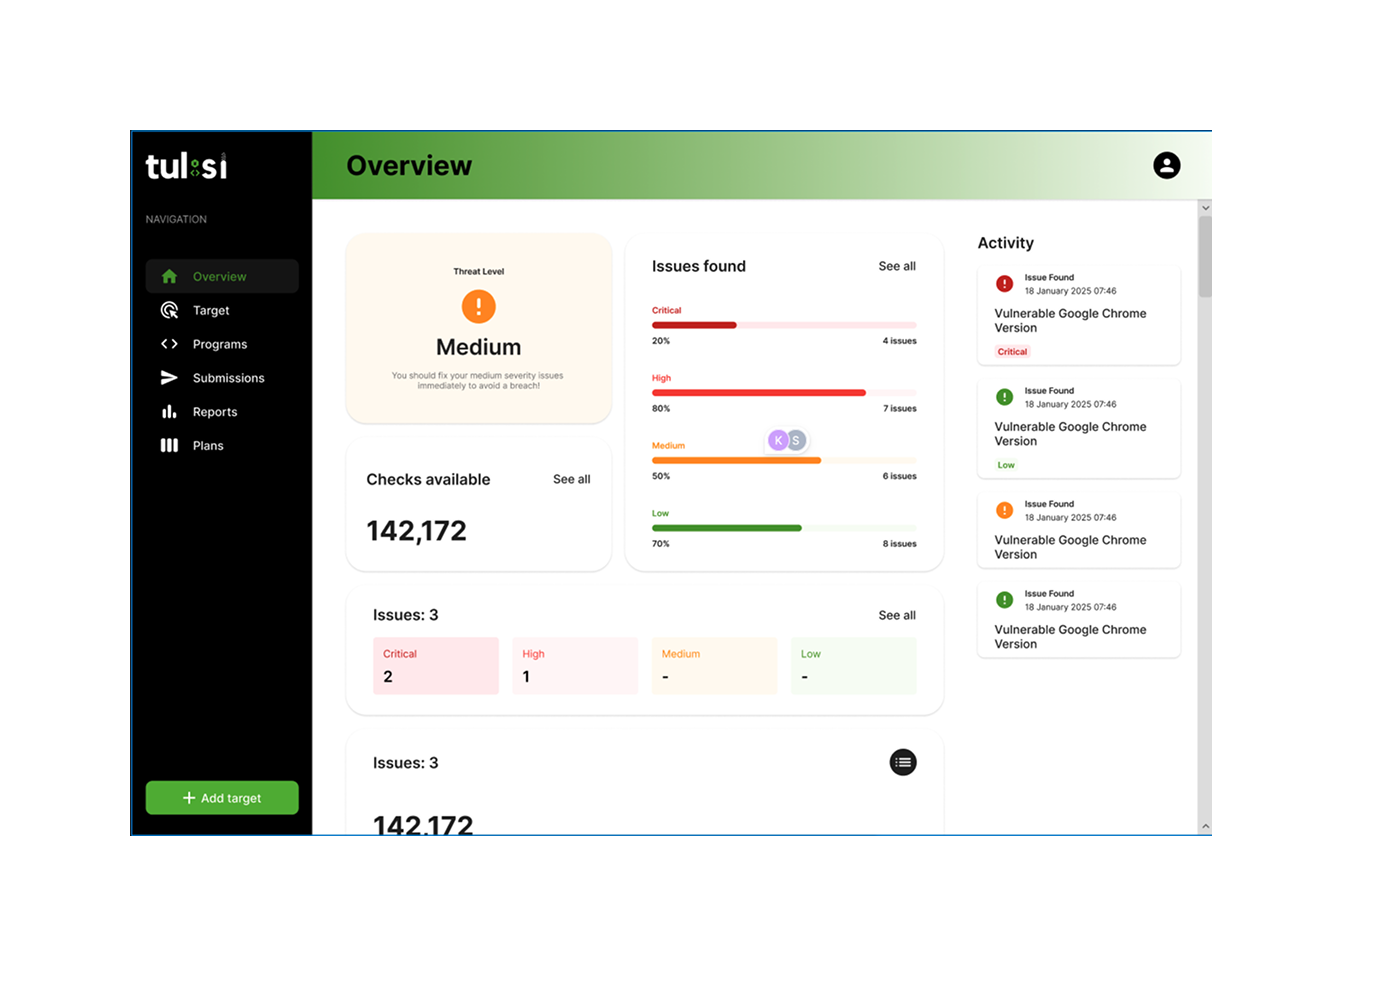
Remediate parameterized queries before next deploy.
CSP and HSTS not enforced on production host.
Disable weak ciphers; verify with rescan after fix.
Point Tulsi at an authorized target, watch the assessment progress, then leave with prioritized findings and remediation language your team can use.
Find issues before they are exploited. Fix with clear guidance. Keep stakeholders aligned.
Point Tulsi at an authorized target and run OWASP-aligned assessments in minutes.
Get prioritized findings with remediation language your team can action.
Export PDFs, rescan after fixes, and keep stakeholders aligned.
Tulsi keeps assessment output tied to remediation — so security and engineering stay aligned from first scan to verified fix.
Register, run assessments on your first domain any number of times, then upgrade when you need more targets.
“Tulsi is a game-changer. Fast, accurate, and essential — the reports helped us fix critical issues before they could be exploited.”
“We’ve tried several tools. Tulsi stands out — intuitive, strong support, and results we can trust.”
“A pentesting solution that’s as powerful as it is easy to use. Highly recommend.”